Tailscale — Zero-config mesh VPN built on WireGuard for connecting your devices
What it is
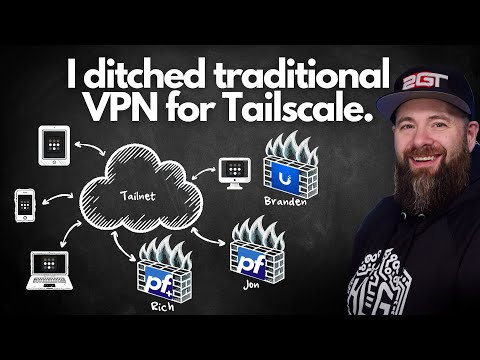
Tailscale is a mesh VPN service built on WireGuard that connects your devices into one private network with minimal setup. Teams and homelab users rely on it to reach servers, NAS boxes and remote machines without opening firewall ports. The trade-off is that device coordination runs on Tailscale's hosted service, so the network depends on it for key exchange and discovery.
Editor's review
Long-form introduction by the BetterPicker editors · checked against the official site · Oct 8, 2026
Tailscale is the VPN for people who do not want to run a VPN: it builds a private mesh network over WireGuard, signs you in with your existing identity provider, and connects your devices without port forwarding anywhere. Clients are open source under BSD 3-Clause, the current release line is 1.104, and the free Personal plan covers up to six users. Paid tiers add user management and compliance features at $8 and $18 per user monthly, with Enterprise custom. You trade some trust in their hosted coordination service for never touching a config file again.
What it does well
Setup is genuinely minutes. Install the client, log in with Google, Microsoft, GitHub, or your company SSO, and your devices can see each other; adding a colleague is sending a link. No firewall rules, no certificate ceremony, no key distribution spreadsheets, which is exactly how it spread through engineering teams by word of mouth.
The WireGuard foundation is a real asset. Tunnels ride a protocol designed for speed and auditability, connections go peer to peer where possible, and the Linux implementation lives in the mainline kernel. Roaming between home, office, and mobile networks is invisible, which is what people actually notice on a Tuesday.
Beyond tunnels, it solves access. Subnet routers expose legacy gear that cannot run the client, exit nodes route all traffic through one place, ACLs define who may reach what, SSH sessions and Taildrop file handoffs come built in, and MagicDNS names every device. Higher tiers add audit logging and device posture.
Who it's for
Distributed engineering teams, homelab builders, small companies without a network team, and developers reaching home machines from anywhere are the core audience. It fits people who want private connectivity without becoming network administrators, and families sharing a tailnet across houses. It fits poorly where policy demands a self-hosted control plane, though self-hosted community alternatives exist to weigh for the determined.
Where it falls short
The coordination service is theirs. Clients are open source, but the control plane that brokers keys and presence is run by Tailscale, which is a trust decision you make once. Your traffic is not readable by them, yet the rendezvous layer is theirs, and policy-minded shops should write that down.
Per-user pricing adds up. The free tier stops at six users, Standard costs $8 per user monthly, and Premium $18, so a forty-person company pays real money while contractors need seats or workarounds. Budgeting it as per-head infrastructure is the honest way to frame it.
Some networks resist it. Restricted corporate networks, some hotel and carrier NAT setups, and jurisdictions that filter VPN traffic can block or degrade tunnels, and the relay fallback trades speed for connectivity. It usually just works; when it does not, your options narrow quickly.
Specs at a glance
Facts from the official site · not editorial opinion
| License | BSD-3-Clause clients; hosted coordination service |
|---|---|
| Price | Personal $0 up to 6 users; Standard $8; Premium $18 per user monthly; Enterprise custom |
| Latest release | v1.104.1 (October 2026) |
| Platforms | macOS, Windows, Linux, iOS, Android |
| Open source | Clients open source; control plane hosted |
| Foundation | Built on the WireGuard protocol |
| Extras | MagicDNS, ACLs, subnet routing, exit nodes, SSH, Taildrop |
Frequently asked questions
▸What is Tailscale?
Tailscale is a mesh VPN service that connects your devices over WireGuard and handles all the key exchange and configuration for you. Log in on each device with your identity provider, and the devices communicate privately as if they were on one local network.
▸Is Tailscale free?
The Personal plan is free for up to six users and a generous device count, which covers most homelabs and families. Paid plans start at Standard, $8 per user monthly, adding unlimited users, ACL groups, and support features for teams and companies.
▸Is it secure if Tailscale runs the coordination service?
Keys are generated on your devices, and the coordination server only distributes public keys and connection details; it cannot read your traffic. The design documents cover this. The residual trust is in the client software and the company's operation of that broker.
▸Tailscale or plain WireGuard?
Plain WireGuard is free and superb but manual: you manage keys, IPs, and peer lists yourself. Tailscale automates all of it and adds identity-based access, naming, and ACLs. Use raw WireGuard for a few static servers; use Tailscale when devices and people change often.
Reviews on YouTube
4 review videos aggregated · praise and criticism included alike · click through to the original video
Channels that covered it
Channels are aggregated as sources only — we don’t rate creators
Related tools

Where to go next
External links open in a new tab; external content is independent of this site.
Link down? Every object page is re-checked monthly.